SecurityCertified

  • Subscribe to our RSS feed.
  • Twitter
  • StumbleUpon
  • Reddit
  • Facebook
  • Digg

Sunday, May 20, 2012

Comparing IEDs and Digital Threats

Posted on 7:41 AM by Unknown
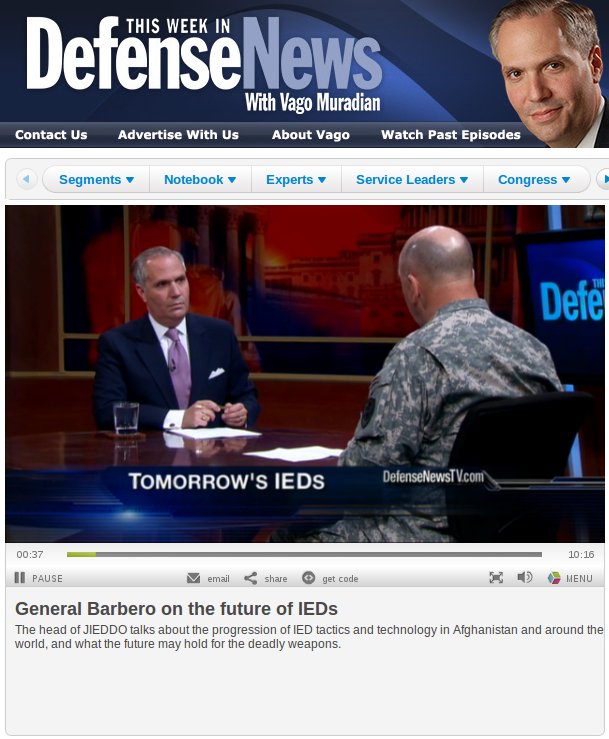
Two weeks ago Vago Muradian from This Week in Defense News interviewed Army Lt Gen Michael Barbero, commander of the Joint IED Defeat Organization. I was struck by the similarities between the problems his command handles regarding improvised explosive devices (IEDs) and those involving digital security professionals.

In fact, you may be aware that papers and approaches like Intelligence-Driven Computer Network Defense Informed by Analysis of Adversary Campaigns and Intrusion Kill Chains by Eric M. Hutchins, Michael J. Cloppert, and Rohan M. Amin, Ph.D. were inspired by the desire to move "left of boom" regarding IEDs.

In this post I will highlight elements from the interview which will likely resonate with those working digital security problems.

  • The threat "shares information globally," and engages in an "arms race" with defenders, sometimes by "sitting in front of a computer" devising the latest tools and techniques.
  • The adversary can introduce changes to tools and techniques in weeks and months, not years or decades as was the case with conventional or strategic weapons.
  • For a "meagre expenditure," the adversary can impose "huge costs on defenders."
  • The goal of the security program (i.e., JIEDDO) is to provide commanders freedom of maneuver to conduct operations (business) in an IED environment.
  • "If you're worrying about the device, you're playing defense." Don't focus only on the device, put pressure on the networks (of adversaries who design, build, and operate the weapons.)
  • Intelligence plays a key role in defeating adversaries. Winning involves applying "lethal pressure, "along with government techniques. "It takes a network to defeat a network."
  • Defeating the device attracts the most attention and funding, but training users and attacking the network must also be pursued. Training involves ensuring that operators are using countermeasures effectively and appropriately.
  • JIEDDO shares threat intelligence in unclassified form so industry partners can devise countermeasures. The unclassified documents are backed by a classified appendix that describes how troops deploy countermeasures in operational settings.
I find the first four minutes of that interview, then comments about unclassified intel sharing at the seven minute mark, to be fascinating. It's clear to me that "malware" is the equivalent to IEDs in this context. Sure enough, just as in the IED world, defeating malware attracts a log of "attention and funding," but training users and "attacking the network" are just as, if not more, important.

If you'd like to see examples of the IEDs encountered in the field and some US countermeasures, check out the first segment.

Tweet

Email ThisBlogThis!Share to XShare to Facebook
Posted in | No comments
Newer Post Older Post Home

0 comments:

Post a Comment

Subscribe to: Post Comments (Atom)

Popular Posts

  • Happy 7th Birthday TaoSecurity Blog
    Today, 8 January 2010, is the 7th birthday of TaoSecurity Blog . I wrote my first post on 8 January 2003 while working as an incident resp...
  • Report on Instances of US Forces Abroad
    Thanks to Steven Aftergood's post Instances of US Forces Abroad I learned of a new Congressional Research Service report of the same na...
  • Security Conference Recommendations
    After my post Bejtlich Teaching at USENIX Security in San Francisco 8-9 Aug a reader asked the following: Richard, I was curious if you cou...
  • I Want to Detect and Respond to Intruders But I Don't Know Where to Start!
    "I want to detect and respond to intruders but I don't know where to start!" This is a common question. Maybe you have a new...
  • Security Onion + (ELSA or Snorby) + CapMe = Awesome
    Happy New Year everyone, and with some new open source software, what a year it will be. Monday Doug Burks released Security Onion 12.04 . P...
  • With "Cyber" Attacks, Effects Matter More Than Means
    I enjoyed reading Stuxnet Poses Interesting International Cyber Law Issues by Rick Aldrich in IAnewsletter Vol 14 No 2 (pdf). I've kno...
  • "Protect the Data" from the Evil Maid
    I recently posted "Protect the Data" from Whom? . I wrote: [P]rivate citizens (and most organizations who are not nation-state ac...
  • Review of Digital Triage Forensics Posted
    Amazon.com just published my two star review of Digital Triage Forensics: Processing the Digital Crime Scene by Stephen Pearson and Richard...
  • Unrealistic "Security Advice"
    I just read a blog post (no need to direct traffic there with a link) that included the following content: This week, I had the opportunity ...
  • Does This Sound Familiar?
    Now that over a week has passed since this Economist article was published, I wanted to cite it and ask if the problem it describes sounds ...

Categories

  • afcert
  • Air Force
  • analysis
  • announcement
  • apt
  • attribution
  • bestbook
  • blackhat
  • books
  • breakers
  • bro
  • bruins
  • certification
  • china
  • cisco
  • cissp
  • cloud
  • clowns
  • commodore
  • conferences
  • controls
  • correlation
  • counterintelligence
  • cybercommand
  • cyberwar
  • dfm
  • education
  • engineering
  • feds
  • fisma
  • freebsd
  • GE
  • ge-cirt
  • hakin9
  • history
  • impressions
  • information warfare
  • ipv6
  • law
  • leadership
  • malware
  • mandiant
  • microsoft
  • mssp
  • nsm
  • offense
  • oisf
  • packetstash
  • philosophy
  • pirates
  • powerpoint
  • press
  • psirt
  • reading
  • redteam
  • reviews
  • russia
  • sans
  • sec
  • sguil
  • snorby
  • spying
  • threat model
  • threats
  • Traffic Talk
  • training
  • tufte
  • tv
  • ubuntu
  • usenix
  • verizon
  • vulnerabilities
  • wisdom
  • writing

Blog Archive

  • ►  2013 (16)
    • ►  September (1)
    • ►  August (1)
    • ►  June (2)
    • ►  April (2)
    • ►  March (1)
    • ►  February (3)
    • ►  January (6)
  • ▼  2012 (60)
    • ►  December (4)
    • ►  November (5)
    • ►  October (3)
    • ►  September (10)
    • ►  August (2)
    • ►  July (6)
    • ►  June (6)
    • ▼  May (4)
      • 5000th Tweet
      • Whistleblowers: The Approaching Storm for Digital ...
      • Comparing IEDs and Digital Threats
      • SEC Guidance Is a Really Big Deal
    • ►  April (2)
    • ►  March (9)
    • ►  February (6)
    • ►  January (3)
  • ►  2011 (108)
    • ►  December (3)
    • ►  November (7)
    • ►  October (11)
    • ►  September (9)
    • ►  August (18)
    • ►  July (10)
    • ►  June (5)
    • ►  May (4)
    • ►  April (13)
    • ►  March (17)
    • ►  February (2)
    • ►  January (9)
  • ►  2010 (193)
    • ►  December (14)
    • ►  November (11)
    • ►  October (6)
    • ►  September (16)
    • ►  August (15)
    • ►  July (26)
    • ►  June (15)
    • ►  May (15)
    • ►  April (15)
    • ►  March (16)
    • ►  February (19)
    • ►  January (25)
  • ►  2009 (123)
    • ►  December (10)
    • ►  November (17)
    • ►  October (21)
    • ►  September (13)
    • ►  August (20)
    • ►  July (21)
    • ►  June (21)
Powered by Blogger.

About Me

Unknown
View my complete profile